Community
3agent
- The full protection layer
- Evidence ledger and verifier
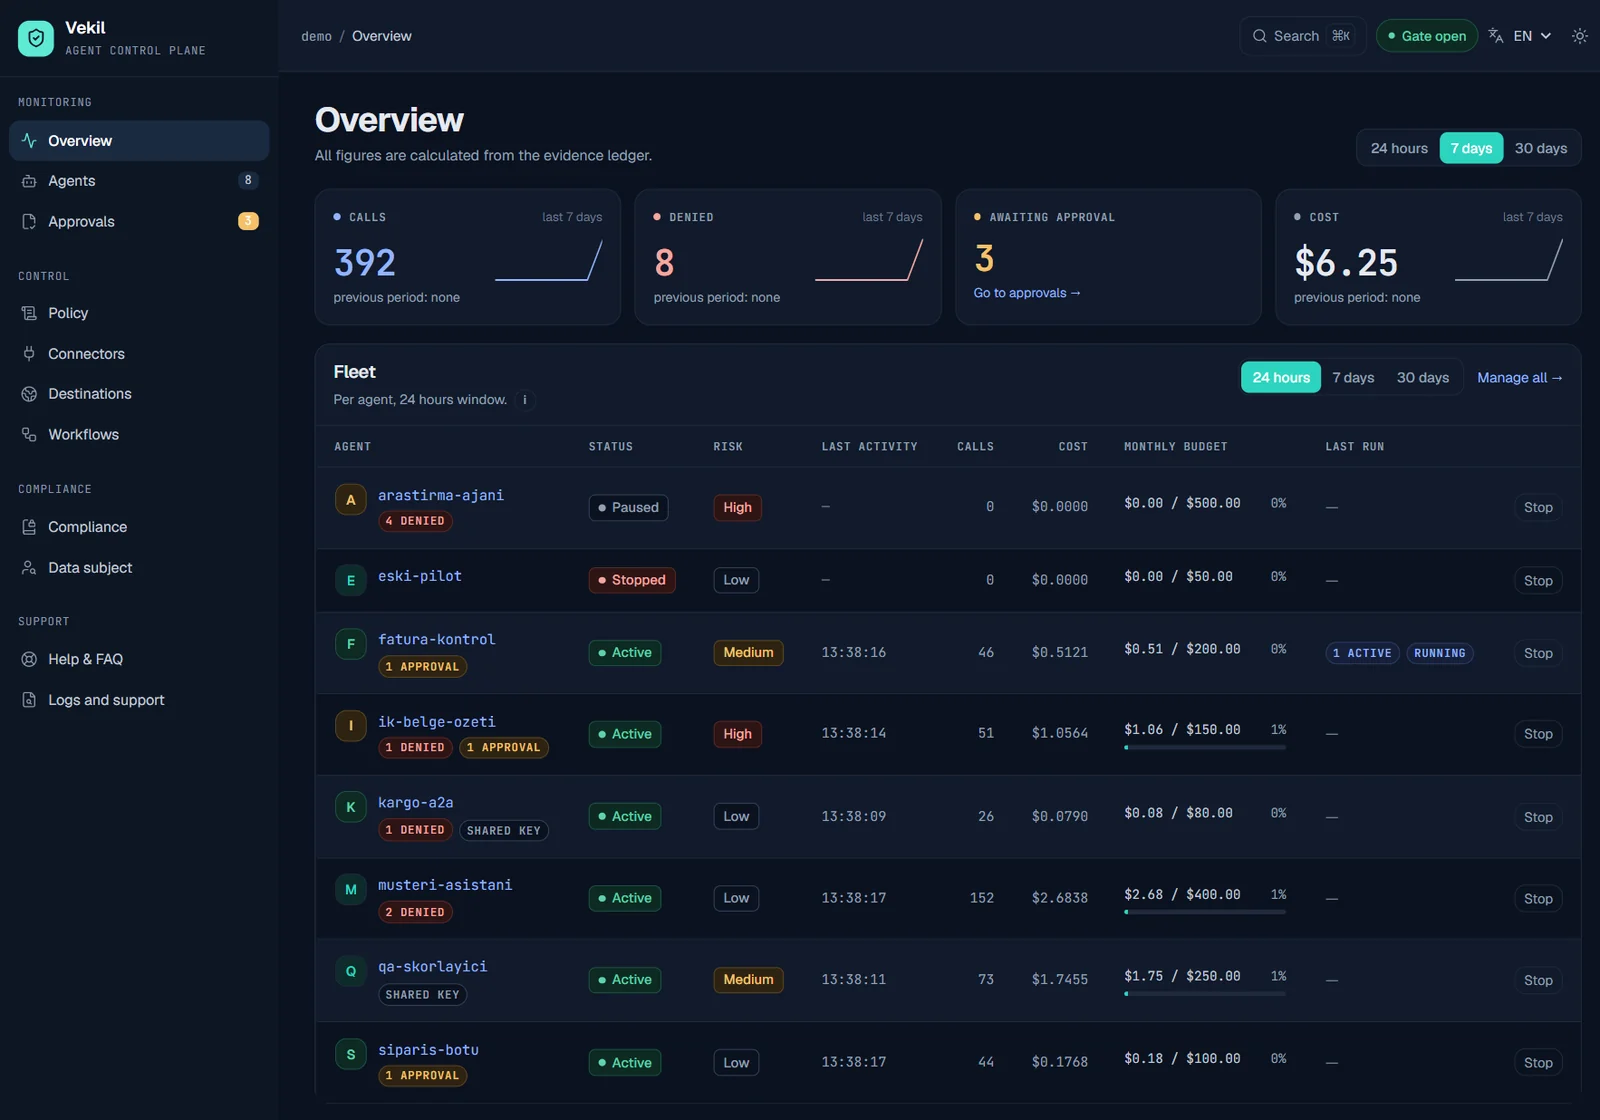
- Overview and fleet dashboard
- Logs and support bundle
What happens if your AI agent sends customer data to a model abroad?
With Vekil: personal data is masked, risky requests come to you for approval, and every step is written to a tamper-evident ledger.
No one knows which agent sent what.
Every call is recorded under the agent's name.
Customer data can leave the country as it is.
Personal data is masked; risky requests come to you.
No evidence to show in an audit.
A tamper-evident, signed ledger that auditors verify offline.
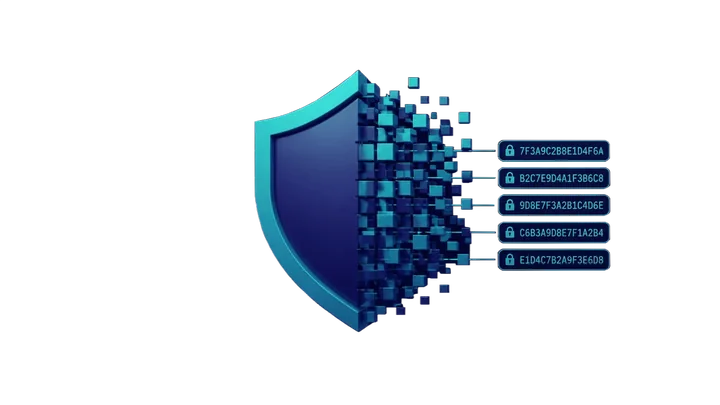
National ID numbers, cards, phone numbers and emails reach the model or external system masked. Personal data never leaves for an unregistered foreign destination. Requests containing an API key, a password or a .env file are not sent at all.
Requests the policy finds risky wait for human approval; the decision can also be made from Teams or Telegram. Any agent or model can be stopped with one click.
Human approval · kill switch
Every call is written to a hash-chained, append-only ledger and signed at the end of the day. Auditors verify the record offline.
Tamper-evident ledger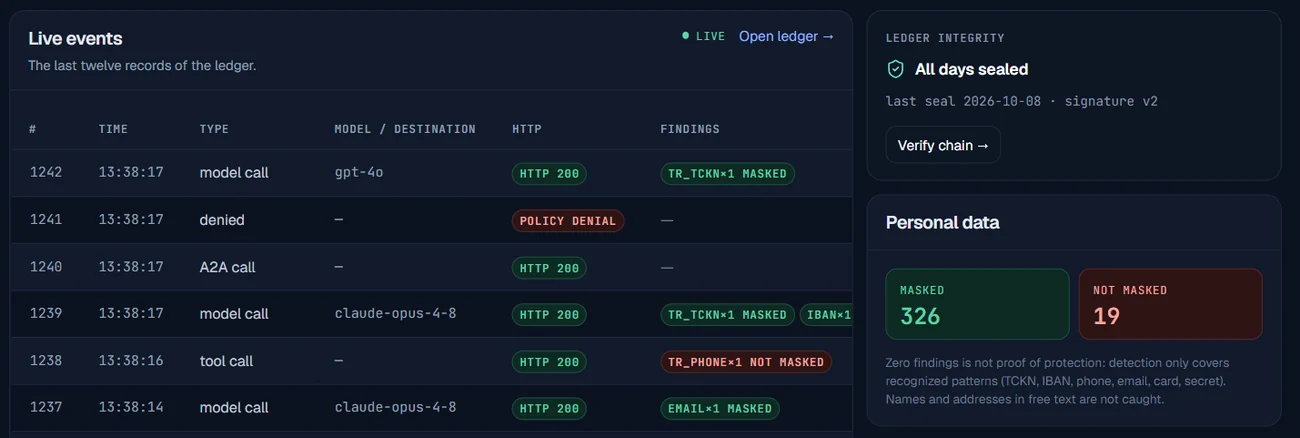
Data masking aligned with KVKK Art. 9, an instant kill switch and a cryptographic audit trail you can verify offline.
Your employees already use AI, most of them with accounts they found themselves. Vekil Chat gives them the company's own chat screen. Every message passes through Vekil's gate.
Write a refund letter for customer Ayşe Y., ID 10000000146, IBAN TR33 0006 1005…
Goes to the model as is. No rule, no approval, no record.
Write a refund letter for customer Ayşe Y., ID <TR_TCKN_1>, IBAN <TR_IBAN_1>
2 personal data items sent masked (national ID, IBAN)
In the Professional and Enterprise editions, with no limit on users.
Vekil inspects the traffic of the agents connected to it. Edit the text below; the masking updates as you type. Add an API key or a DB_PASSWORD=… line and see what happens.
This request is NEVER sent to the model: it contains a secret (API key, password or private key). Vekil rejects it and writes the denial to the ledger.

What would reach the model without the secret:
Summarise this customer refund request:
ID <TR_TCKN_1>, phone <TR_PHONE_1>
Email: <EMAIL_1>
Refund IBAN: <TR_IBAN_1>
Card: <CREDIT_CARD_1>
DB_PASSWORD=<SECRET_1>
This box runs in your browser; nothing you type is sent anywhere. It is a small sample of Vekil's full recognizer.
One-minute videos recorded in the real product with demo data. All are subtitled, so they work with the sound off.
A one-minute animation: agents, the gate, masking, human approval, the evidence ledger and Vekil Chat.
Every number on the dashboard is computed from the evidence ledger.
National ID, phone and email reach the model masked.
The agent waits for approval; a misbehaving agent stops within a second.
Your applications connect to Vekil with their existing SDKs. Model calls, API requests and MCP tools all pass the same checks.
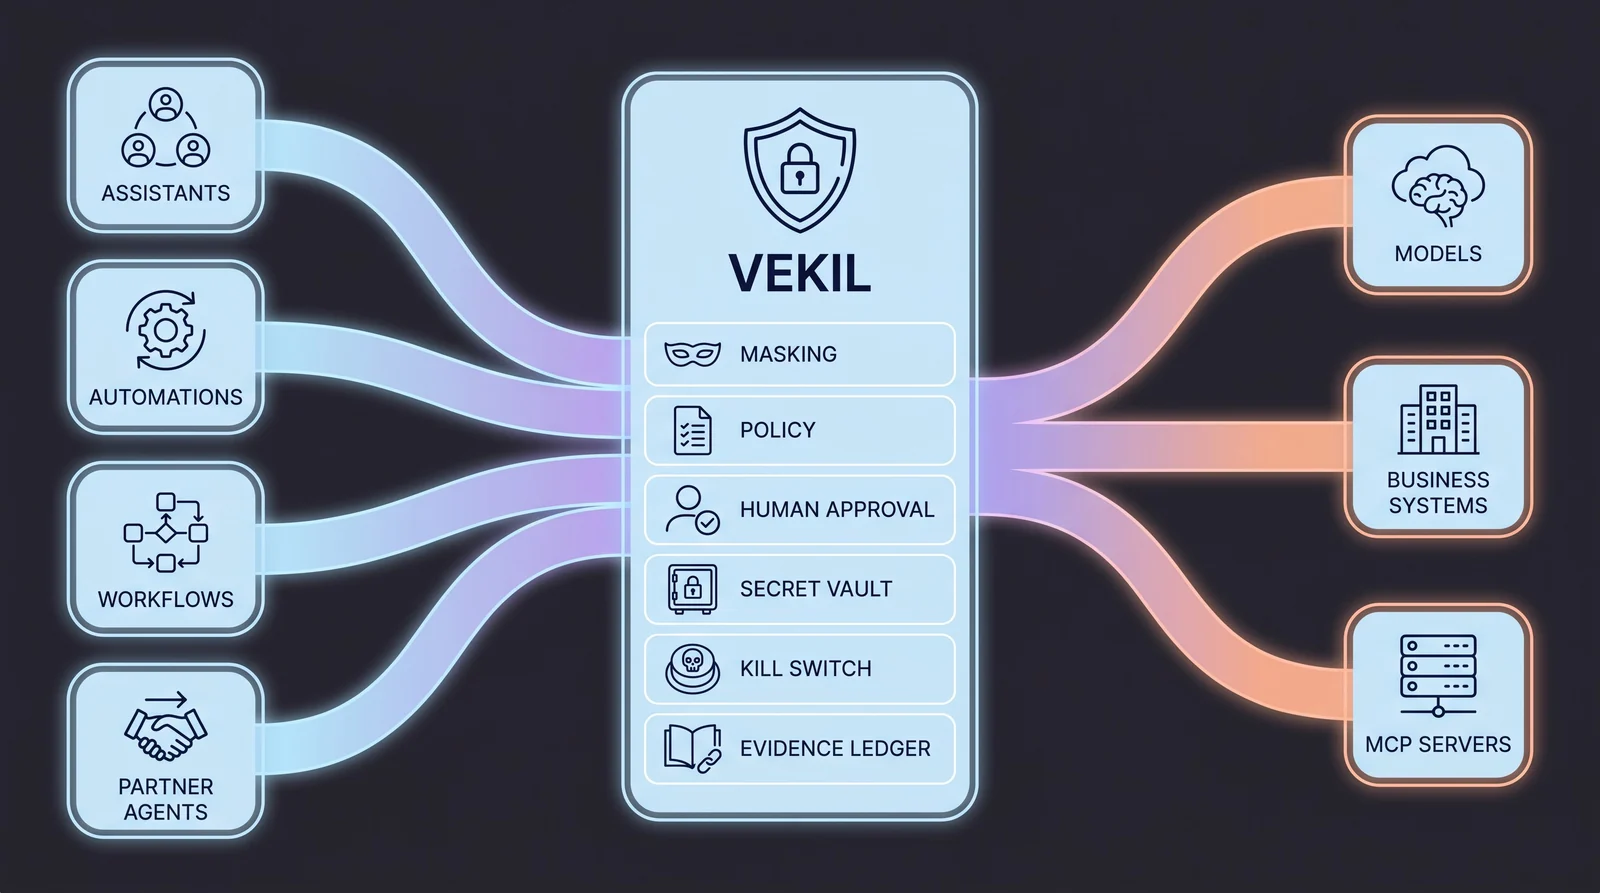
Editions differ in the number of agents and in compliance, reporting and integration features.
Protection is on in every edition. Masking, policy, the transfer gate, human approval, the kill switch and the evidence ledger work regardless of license. Traffic keeps flowing even if a license expires.
We'll show you how it works with your own agents and your own data.